GitLab Secrets Manager adds ESO, Terraform, API support
Today, you might maintain separate secret stores for CI/CD, Kubernetes, and Terraform. However, that leaves multiple tools to manage, access
Today, you might maintain separate secret stores for CI/CD, Kubernetes, and Terraform. However, that leaves multiple tools to manage, access
Static scanners excel at catching vulnerabilities that fit a known pattern, like unsanitized query inputs, hardcoded secrets, and unsafe deserialization.
AI is writing more code and pulling in more dependencies, increasing application risk. Most of that exposure isn’t from code
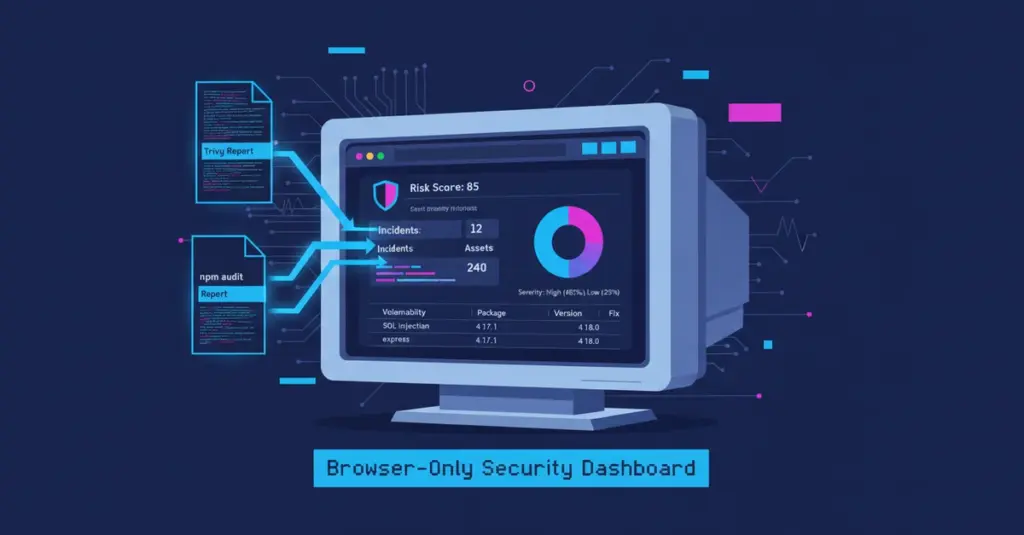
****When working with security tools like “Trivy” and “npm” audit, I realized that their primary goal is to generate detailed
Most enterprises use a handful of different security scanners, each configured and enforced, project by project. With no single view